Showing posts with label Botnet Research. Show all posts

Tuesday, February 4, 2014

POS Malwares On The Rise - BlackPOS Attacking Point-of-Sale Devices Yet Again !


POS malwares has been on the rise since last few quarters . We've been witnessing increasing volume of the malwares targetting Point of Sale devices . These malwares primarily get installed on the windows terminals used as point of sale in the stores , enumerates the process memory and reads the track1 / track2 information from the RAM as and when terminals reads the information embossed in the megnetic strips of the card. This information is the sent back to the C&C server. Apparently , tt could be used by the attackers to clone the card with the same information and further , embossing equipments like CC embosser / Printer / writer machines readily available in the market can be used to make the cards look like the original one . I blogged about one of the similar attack in the past called Vskimmer .

Another attack named BlackPOS very similar to this has been around for a while targetting the Neiman Marcus and Target stores compromising almost 110 Million customers. Neiman Marcus group confirmed this attack :


This has extensively been talked about in the blog post by Xylibox over here. I've had a look at one of the sample related to this attack to see how it exfilterates the stolen information. One of the way malware is found to be generating the network traffic is by executing the commands via "PsExec" sysinternals tool . PsExec is the utility to execute the processes on the remote system. It can invoke the command prompt on the remote systems as well .

BlackPOS connects to the SMB share on the hardcoded IP address 10.116.240.31 which is kind of presumed to be the internal subnet IP of the targetted stores and executes the taskkill command invoking the command shell on the remote system.


It creates the log file with the name of the current system time and date . For instance during the time of execution of this malware it created the file with the name data_2014_2_3_16_11 . It drops the txt file "cmd.txt" in the same directory with the list of commands it would execute from the command shell while opening the FTP connection to the C&C server . Below you can notice the "open" command being used . This can be fired from the command prompt after entering the FTP shell prompt .


Below screenshot shows the dropped cmd.txt file with all the ftp commands along with username and password :


and then eventually launches all the above commands from the cmd shell


All the commands as and when executed are also being logged on the console


While looking at the multiple samples for BlackPOS , we've came across several different IPs being connected to via FTP . However , data exfilteration has been not found to be done via any other protocol.

Point of Sale malwares also nicknamed as RAM Scrappers are increasing in the last few quarters . Apparently one of the reason to directly target the sale devices is its ease of implementation rather than employing the sophisticated traffic interception and hooking methods which has become the history now.

Saturday, November 2, 2013

Periodic Command Pull From C&C Servers Paves The New Way to Detect Botnets


HTTP has been predominantly used by recent botnets and APTs as their primary channel of communication with the Command and Conrol servers . This number has significantly shown increase in the last few quarters. One of the research shows  that more than 60% of the botnets use HTTP protocol to achieve C&C communication and the number has kept increasing. Below distribution shows the popularity and dominance of HTTP protocol among the top botnet families.


Couple of  apparent reasons to use HTTP as a primary channel for C&C is that it cannnot be blocked on the network since it carries major chunk of the internet traffic today . Secondly , it is not hard , but nearly impossible to differentiate the legitimate HTTP traffic from the malicious one on the network perimeter unless you have the known signatures for it. This makes HTTP even more popular among malware authors.

Industry is well aware of the fact that traditional signature based approaches are no longer a solution to today's sophistication level of the threats and limitations with this has driven the shift of focus from signatures to behaviour. But we need to answer the question : What are those suspicious behaviours we should look for on the network ?

Before we answer that question , I'd like to throw some light on the typical lifecycle of botnet command and control over HTTP.

  • Botnets would typically connect to a small number of C&C domains . It may try to resolve too many domains over the short period of time when it does DGA kind of stuff , but once it successfully resolves a domain and connects, it will stay connected to the same domain for its lifetime
  • Once connected , it will send either HTTP GET / POST request to the specific resource ( URI ) of the C&C server as the registration / phone home communication.
  • It will execute the command received from the C&C server OR will either sleep for the fixed interval of time before connecting back again and pull the command from C&C.
  • Subsequently, it will connect to the server at fixed / stealth intervals and will keep pulling commands or might send keepalive messages to announce its existance periodically.
What we learn out of this behaviour is that botnets typically work in a “pull” fashion; they continuously fetch commands from the control server, either at fixed intervals or at stealth level . Quick example to demonstrate this behaviour is Zeus . Below is traffic snapshot of Zeus communicating with control server every 6 seconds.

Zeus C&C communication over the network


We realize that machine infected with botnet communicating with the control server periodically is the automated traffic . Since this behaviour can also be exhibited from the legitimated software and websites, another questions comes up here : How do we differentiate browser / human initiated traffic from the automated traffic ?  Certain facts that we can definitely rely on : 
  • It is abnormal for most users to connect to a specific server resource repeatedly and at periodic intervals. There might be dynamic web pages that periodically refresh content, but these legitimate behaviors can be detected by looking the server responses.
  • The first connection to any web server will always have response greater than 1KB because these are web pages. A response size of just 100 or 200 bytes is hard to imagine under usual conditions.
  • Legitimate web pages will always have embedded images, JavaScript, tags, links to several other domains, links to several file paths on the same domain, etc. These marks the characteristics of the normal web pages.
  • Browsers will send the full HTTP headers in the request unless it is intercepted by MiTM tools that can modify / delete headers.
All of the above facts allows us to think about the specific behaviour we can look on the network : Repetitive connections to the same server resource over HTTP protocol

Assume that we choose to monitor a machine under idle conditions–when the user is not logged on the machine–we can distinguish botnet activity with a high level of accuracy. We think about monitoring the idle host because that's the period where the traffic volume is less. It is kind of relatively easy to identify idle host due to the nature of the traffic that it generates ( usually version updates , version checks , keepalives etc ..). We 'd never expect the idle host to generate traffic to yahoo.com or hotmail.com.

Under these conditions , if the machine is infected with Spyeye botnet , traffic will look like this:


Notice that Zeus ( in the previous screenshot ) / Sypeye connects to one control domain and keeps sending HTTP POST every 6 and 31 seconds respectively to a specific server resource. Algorithmically, while idle, we’d deem a host's activity suspicious when :
  1. The number of unique domains a system connects to is less than a certain threshold
  2. The number of unique URIs a system connects to is less than a certain threshold
  3. For each unique domain, the number of times a URI is repetitively connected to is greater than a certain threshold
Assuming the volume of traffic from the host is less, If we take the preceding conditions in a window of say two hours, we might come up with following:
  1. Number of unique domains = 1 (less than the threshold)
  2. Number of unique URIs connected = 1 (less than the threshold)
  3. For each unique domain, the number of times a unique URI is repetitively connected to = 13 (greater than threshold)
 The approach however, does not mandates that repetitive activity should be seen at these fixed intervals. If we choose to monitor within a larger window, we could detect more stealthy activities. The following flowchart represents a possible sequence of operations.


The first few checks are important to determine whether the host isn't talking too much. First, Total URI > threshold determines that we have enough traffic to look into. Next, Total Domain access >/= Y determines that the number of domains accessed is not too large. The final check is to see if Total unique URIs < Z. The source ends up on the suspicious list if we believe it has generated repetitive connections.

For instance, if the Total URIs = 30, Total Domain access = 3, and Total Unique URI accessed = 5, we guarantee a repetitive URI access from the host. Now if the number of repetitive accesses to any particular URI crosses the threshold (for example, 1 URI accessed 15 times within a window), we can further examine the connection and apply some of heuristics to increase our confidence level and eliminate false positives. Some heuristics we can apply:
  • Minimal HTTP headers sent in the request
  • Absence of UA/referrer headers
  • Small server responses and  lacking structure of usual web page
  • Domain registration time and perhaps reputation as well.
Let’s look at an example of SpyEye sending minimal HTTP headers without a referrer header:


I implemented the proof of concept for this approach and I could detect the repetitive activity with relative ease.


Applying this method over several top botnet families exhibiting similar behaviour , I could detect them with medium to high level of confidence.


Behavioral detection methods will be the key to detecting next-generation threats. Given the complexity and sophistication of the recent advanced attacks, such detection approaches can address threats proactively–without waiting for signature updates–and will prove to be much faster.

Wednesday, June 5, 2013

Citadel Botnet Logs With Bank Account Logins On a Sale In Underground Forums


Financial theft is one of the most lucrative forms of cybercrime. Malware authors continue to deliver sophisticated tools and techniques to unlock online bank accounts. Attackers design and develop botnets to perform financial fraud, targeting banks and other institutions for profit. These botnets traditionally have monitored victims’ Internet activities and intercepted banking transactions to extract account credentials and send them to their control servers. Recent botnets are armed with more advanced capabilities, yet traditional methods continue to be the most effective way to steal money.

Recently I came across an underground Russian forum in which an author was actively selling botnet logs with account-login details from one targeted bank.


These botnet logs were from the Citadel botnet Version 1.3.4.5 (Extreme Edition). Citadel is a variant of the popular Zeus botnet and has been widely seen since late 2012. The latest edition of this botnet has already been covered in several blogs out there.

Here is a snapshot of server code for extracting bank account information stored in the database of the C&C server.


Here is what this mysterious banking botnet can do.It can log all the credentials used to login into the bank account , from the Citadel infected machine and sends it to the C&C server.


Research has revealed that Citadel is one of the most active botnets in the world, spanning several locations across Europe. One of the major reasons for its common use is that the botnet setup services are fairly cheap via the underground community. Here is an advertisement for the Citadel setup service.


Same user advertising his setup service on another forum.


Yet another service offered for the same botnet.


Many cybercriminals avoid transferring money to their own accounts due to the risk of prosecution, but selling the account information and making the money from the sale is an effective way of preserving  anonymity. Thus the attacker can’t be held accountable for the transfers made from a stolen account.
As the precautionary measure, we should look out for accounts being accessed or transactions made to/from different geographical locations. Banks place limits on the amount of money that can be transferred in one day or in a single transaction. Spotting small, unauthorized transactions made from an account should be noticeable and prevent major financial losses.

Sunday, April 28, 2013

VSkimmer Botnet Targets Point-Of-Sale Devices : Be Cautious When You Swipe Your Credit Cards Next Time For Shopping !!..


I was monitoring one of the Russian underground forums a while back, and came across a discussion thread  where the author was offering the malware for sale which had the capability to steal the credit card information from the Windows machines attached the Credit / Debit card payment devices.This malware, vSkimmer, can detect the card readers, grab all the information from the Windows machines attached to these readers, and send that data to a control server. These kind of equipments are typically known as Point-Of-Sale devices used for processing the Credit / Debit card financial transactions and are used in shops , hotels and other industries . The author of the thread also discusses other capabilities of this malware, which appears to be a successor of Dexter discovered last year , but with additional functions.


Later in the thread , author of this malware discusses about the payment methods and the sale policies.


We already know about botnets such as Zeus , SpyEye , Citadel  ( variant of Zeus ) which performs financial fraud using extremely sophisticated techniques including  intercepting the victims’ banking transactions. VSkimmer is another example of how financial fraud is actively evolving and how financial Trojans are developed and passed around in the underground community. This botnet is particularly interesting because it directly targets card-payment terminals running Windows.

I analyzed  samples of this malware and figured out how it steals the credit card information and its additional control functionalities as well. While performing the API tracing , we found it uses fairly standard antidebugging techniques .


The malware collects the following information from the infected machine and sends it to the control server:
  • Machine GUID from the Registry :
  • Locale info
  • Username
  • Hostname
  • OS version


This malware uses a standard installation mechanism and copies itself as svchost.exe into %APPDATA% , modifies the registry key to add itself under the authorized list of apps, and runs ShellExecute to launch the process. One function of vSkimmer if the Internet is not available is to wait for a USB device with the volume name KARTOXA007  to be connected to the infected machine and to copy all the logs with the file name dumz.log and the card info collected from the victim to the USB drive.


As you can notice in the above code , it tries to resolve the C&C server www.posterminalworld.la and if it does not resolve , it will call another subroutine to wait for the USB drive to be connected and copies the collected logs.


I checked by disconnecting from the Internet. The malware enumerated all the drives and created the file dumz.log in the drive with the preceding name.


Extracting Credit Card numbers from the memory

VSkimmer maintains the whitelisted process, which it skips while enumerating the running processes on the infected machine.


Once vSkimmer finds any running process not in the whitelist, it executes  OpenProcess and ReadProcessMemory to read the memory pages of the process and invokes the pattern-matching algorithm to match the regular expression “?[3-9]{1}[0-9]{12,19}[D=\\u0061][0-9]{10,30}\\??”)” and extract the card info read by the payment devices. This is done recursively for every process running in the infected machine and not on the whitelist and continues doing it as long as the malware runs inside the system.


Vskimmer Network Communications

Before communicating with the command and control server, the malware B64-encodes all the machine information collected and appends it to the URI. The encoded string follows this format:

machine guid|build_id|bot_version|Windows_version|Host_name|User_Name


While this malware ran, we saw the following response. Note that the commands are within the tag.


Once vSkimmer receives a response from the server, it executes the following routine to parse the command:


Because the response from the server during execution was null, the malware extracts the 3-byte command and tries to match it with the other commands implemented by vSkimmer. First it checks if the command from the server is “dlx.”


If not, then vSkimmer checks for the “upd” command. These commands implement the HTTP download and execute (“dlx”) and update of the bot (“upd”), respectively.

As we saw earlier in this post, vSkimmer can also grab the Track 2 data stored on the magnetic strip of the credit cards. This track stores all the card information including the card number. (You can read more about the Track 2 data format on Wikipedia. In summary , the data stored is : 
  • Primary Account Number : The number printed on the front of the card
  • Expiration Date
  • Service Code: the three-digit number

Vskimmer botnet Control Panel


Monday, August 27, 2012

Inside The DDoS Botnets - BlackEnergy and Darkness - Part 2


Darkness bot – Successor of BlackEnergy

Recently in the December last year , we came across a new DDoS bot found to be fairly active in the wild targetting number of websites . During our analysis , the samples of bots were using particularly 3 domains as their command and control channnel.

greatfull-toolss.ru
greatfull.ru
hellcomeback.ru


However , couple of domains out of these were already unavailable , querying the whois database for greatfull.ru gives the following whois record :

nserver:    ns1.reg.ru.
nserver:    ns2.reg.ru.
state:      REGISTERED, DELEGATED, UNVERIFIED
person:     Private Person
phone:      +380686548525
fax-no:     +380686548525
e-mail:    
 smilefrince@yandex.ru
registrar:  REGRU-REG-RIPN
created:    2010.11.03
paid-till:  2011.11.03

Googling for the above email address used for registering the domain showed up several adds related to the DDoS service. One of the add that we came across displayed the services and capabilities this botnet can provide.


Darkness bot command and control

During our investigation , we came across the C&C UI used to track the botnet infections and instruct the DoS commands to the bot client . One of the control panel we observed posted on the underground forums looked like this: 


Above control panel UI is in the Russian language , However , we have been able to translate and understand the purpose of quite a few commands through our command simulation setup Following are the DDoS commands used by this Bot .

exe --- > download specified binary from the server
dd1 --- > HTTP GET DDoS attack
dd2 --- > ICMP DoS attack
wtf  --- > Stop all the commands
tot   --- > Bot synchronization time . 
vot  --- > Voting

During our static Analysis , we were able to unpack the and reverse the binary during which we located the Command and Control code within the  binary and some other functionalities which gives us the fair enough idea on how the malware runs on the victims system .

Below is the code segment for one of the command and action it takes if the command matches. After checking the command , it calls the same routine multiple times and calls the CreatThread API to initiate the DoS attack.


Above unpacked view of the binary just gives an idea of 3 hardcoded encrypted+B64 encoded URLs, the string “darkness” , copies itself as dwm.exe and runs as IpSectPro service.

Network communications with the bot client


During our extensive research on this Bot , given that we had an idea of how the command format of the bot looks like , we were able to simulate the DDoS attack . Once executed , client sends the Registration request to the control server and we were able to make the server reply with the B64 encoded DoS command as shown below :


Decoded command is an instruction to DoS the websites

dd1=http://www.abc.com/;http://www.xyz.org

And we were able to see the DoS attack initiated from the client . Within the span of 5 minutes , we were able to see approximately 80,000 hits logged on the server .


Next , we also simulated the ICMP DoS attack . We made the server reply with the “dd2” command to be able to see the ICMP DoS. Server response in this case was as below.

HTTP/1.1 200 OK
Date: December 13, 2010 2:47:53 AM PST
Server: Xerver/4.32
Connection: close
Content-Type: text/html
ZGQyPWh0dHA6Ly93d3cuYWJjLmNvbS87aHR0cDovL3d3dy54eXoub3Jn

Above B64 command when decoded :  dd2=http://www.abc.com/;http://www.xyz.org which initiated the ICMP DoS.


Inside The DDoS Botnets - BlackEnergy and Darkness - Part 1


BlackEnergy was very popular DDoS bot which used to prevail couple of years back . This bot has been under development and has evolved since quite some time with its successor named Darkness bot with the similar abilities.This Bot has evolved with new features continuously added to extend its malicious capabilities . Researchers have been keeping an eye on this and analysis of the Command and Control(C&C) traffic of the bot samples existing in the wild has revealed that this bot should be a product of the Russian Cyber market , while the traces indicating  the same have been found within the bot executables as well.

This bot comes with a variety of DoSing capabilities and has been observed to be targeting the Russian Websites. Recently, during our Investigation, we managed to get access to the BlackEnergy builder toolkit which unlike previous available builder versions , comes with the option of building the polymorphic binaries to bypass AV detections and also includes anti-debugging features. The toolkit comes with the root directory www/ which includes the PHP scripts for controlling the Bot and other details such as MySQL database schemas which gives fair enough idea on the architecture of the Botnet.

This blog  provides detailed analysis of the BlackEnergy bot builder toolkit. We will also examine the server side PHP scripts to understand the bot command and control channel. Additionally we will also analyze the DDoS traffic generated by the bot. Later part of this series also sheds some light over the recently emerging Darkness bot which is believed to be related to BlackEnergy and has overshadowed BlackEnergy in terms of its DoSing capabilities.

BlackEnergy DDoS Bot builder:


Above screenshot is of the builder toolkit used to build the bot client which is then usually downloaded by victims through drive-by-downloads or distributed through Spam e-mails.

Below are all the default parameters used to build the bot client and as such most of the parameters are very well self explanatory.

Host             : C&C Server communicating with the bot client .
Request Rate         : Specifies the time interval after which new command should be      fetched from the C&C server.
Build ID                : Unique Build ID for each bot . This will change every time the builder  tool kit  is invoked.
Default Command : Command to execute if bot client cannot connect to the C&C server.
Execute after        : Time after which command should be executed.
Outfile                  : Final bot client executable name

Default DDoS parameters

ICMP Freq  : No. of ICMP packets to send in the attack.
ICMP Size   : Size of the ICMP packets in the attack.
Syn Freq     : No. of SYN packets to send in SYN flood 
HTTP Freq : No. of HTTP Request to send in the HTTP flood 
HTTP Threads : No. of HTTP threads to create during the attack.
TCP /UDP Freq : No. of TCP / UDP packets to send during TCP / UDP flood attack.
TCP Size    : Size of the TCP payload.
UDP Size   : Size of the UDP payload.
Spoof IP’s  : Boolean value to enable or disable IP Spoofing during the flooding.
Use Crypt traffic  : May be used for encrypting the bot client communication.
Use polimorph exe : Inserts different encryption routines to bypass AV detection.
  and antidebug

After specifying all the configuration options, clicking on “Build” button will output the bot client which is then distributed through various means

Server Side Botnet Command and Control System :

The toolkit comes with the C&C server side PHP scripts which interacts with the MYSQL database at the backend to track the bot infections. We’ve observed the  following files in the toolkit .
§   
     Auth.php               
§     Config.php
§     Index.php
§     MySQL.php
§     Stat.php
§     db.sql
    Readme.txt

Let’s understand the code in each of these files and learn how the system works altogether.

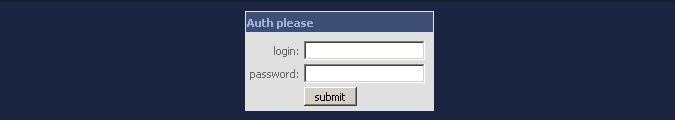
The C&C system comes with the basic HTTP password authentication scheme. Auth.php presents the Login/Password screen from where the Botnet can be further controlled by the Bot Master.


Admin and MySQL Login details are saved in the config.php file as below.
         // íàñòðîéêè áàçû
         $opt['mysql_host'] = "localhost";
         $opt['mysql_user'] = "b0t2";
         $opt['mysql_pass'] = "2413038";
         $opt['mysql_base'] = "b0t2";

          // ëîãèí è ïàññ ê àäìèíêå
         $opt['admin_pass']  = "admin";
         $opt['admin_login'] = "132";
?>

Bot C&C system has a pretty simple database schema with the SQL queries in the db.sql file. Following is an excerpt  from that file.
--
-- Table structure for table `opt`
--

CREATE TABLE `opt` (
  `name` varchar(255) NOT NULL,
  `value` varchar(255) NOT NULL,
  PRIMARY KEY  (`name`)
);

“Opt“ table has the following name and its default values which is displayed on the UI when index.php is accessed.

--
-- Dumping data for table `opt`
--

INSERT INTO `opt` (`name`, `value`) VALUES ('attack_mode', '0'),
('cmd', 'wait'),
('http_freq', '100'),
('http_threads', '3'),
('icmp_freq', '10'),
('icmp_size', '2000'),
('max_sessions', '30'),
('spoof_ip', '0'),
('syn_freq', '10'),
('tcpudp_freq', '20'),
('tcp_size', '2000'),
('udp_size', '1000'),
('ufreq', '1');
-- --------------------------------------------------------

db.sql  also has the important table structure , “stat” used for tracking the size of the botnet. All the data that is POSTed by the bot client is logged in this table along with the Build ID which is sent back by the bot client to the C&C system .

--
-- Table structure for table `stat`
--

CREATE TABLE `stat` (
  `id` varchar(50) NOT NULL,
  `addr` varchar(16) NOT NULL,
  `time` int(11) NOT NULL,
  `build` varchar(255) NOT NULL,
  PRIMARY KEY  (`id`)
);

Index.php is the script that connects to the SQL database and fetches the statistics which are displayed on the GUI. Following SQL queries are found in the index.php file  

$r = db_query("SELECT * FROM `opt`");   while ($f = mysql_fetch_array($r))        $opt[$f['name']] = $f['value'];

$r = db_query("SELECT COUNT(*) AS `cnt` FROM `stat` WHERE ".time()."-`time`<".($opt['ufreq']*60));  $btotal = intval(mysql_result($r, 0, 0));

$r = db_query("SELECT COUNT(*) AS `cnt` FROM `stat` WHERE ".time()."-`time`<".(60*60));  $bhour = intval(mysql_result($r, 0, 0));

$r = db_query("SELECT COUNT(*) AS `cnt` FROM `stat` WHERE ".time()."-`time`<".(60*60*24));   $bday = intval(mysql_result($r, 0, 0));

$r = db_query("SELECT COUNT(*) AS `cnt` FROM `stat`");
  $ball = intval(mysql_result($r, 0, 0));   $builds = array();

$sql = "SELECT COUNT(*) AS `cnt`, `build` FROM `stat` GROUP BY `build`";
$r = db_query($sql);


Botnet Commands

We have reverse engineered C&C code on the bot client and have identified that it comes with 3 major type of commands. Arguments to these commands are also documented in the Readme.txt and cmdhelp.html files  accompanying this package in the Russian language . During our analysis of the bot client binary , we’ve also found the 4th command which is not documented in the help files. Let ‘s understand each of the command and its binary code

A )  flood :-

“Flood” command instructs the bot client to initiate several different types of flooding attacks Arguments to this command instructs the bot about the type of flood attack to generate along with the other parameters as shown earlier Figure 1 . Arguments to the type of flooding attacks can be following:
-      ICMP
-      UDP
-      SYN
-      HTTP
-      Data

Flood command along with the arguments and other parameters are sent by the server to the bot client in Base-64 encoded format . Below is an example of the decoded command indicating  how the bot client is instructed to carry out a TCP SYN flood on port 80:

4500;2000;100;1;0;30;500;500;200;1000;2000#flood syn mail.ru 80 #10#xEN-XPSP1_80D1F15C

B )  stop :-

Stop command instructs the bot client to temporarily stop DDoS floods for the specified number of seconds

C )  die :-

Die command instructs the bot client to delete itself from the infected system. It calls the ExitProcess API to terminate the process and stop all DDoS activities.

PUSH 3
PUSH _bot.15111484        ;  ASCII "die"
MOV EAX, [ARG.1]         ;  _bot.
PUSH EAX
CALL _bot.151154C0
ADD ESP, 0C
TEST EAX, EAX
JNZ SHORT _bot.15112C2A
CALL _bot.151127B0
PUSH _bot.15116900          ; /FileName = ""
CALL DWORD PTR DS:[<&KERNEL32.DeleteFileA>]   ; \DeleteFileA
PUSH 0                                        ; /ExitCode = 0
CALL DWORD PTR DS:[<&KERNEL32.ExitProcess>]   ; \ExitProcess

E )  wait:-

This command instructs the bot client to remain silent without performing any activity and contact the C&C server for new commands after the specified interval. Format of this command is as shown below :

 4500;2000;100;1;0;30;500;500;200;1000;2000#wait#10#xEN-XPSP1_80D1F15C

This instructs the bot client to wait for 10 minutes before checking for new commands . This is exactly what can be figured out from the screenshot below 


Network Communications:

BlackEnergy Bot client uses HTTP protocol to communicate with the C&Cserver. It uses HTTP POST request to stat.php page as shown in the "Architecture of Botnet" section. POST request data is then logged into the “stat” table in the database primarily used for tracking the bots.

The information sent by the bot-client in the HTTP POST request message includes the ID and the build ID.

ID parameter is a combination of the SMB hostname and the C:\ volume information of the infected machine. The code section below shows how the ID parameter is built


Build_ID is the parameter which is randomly generated by the bot builder and is probably used to track the botnet infections.
In reponse, the C&C server replies with the Base-64 encoded command as shown below.


The decoded command shows the following:

4500;2000;100;1;0;30;500;500;200;1000;2000#wait#10#xEN-XPSP1_80D1F15C.

This shows the extent upto which the DDoS parameters are configurable in this bot. All the parameters are present even in the #wait# command. Likewise, variety of different DoS commands can be given by C&C sever, few of which are listed below:

# flood syn www.abc.com 25#10#
# flood http www.xyz.com#20#
# flood udp;dns;syn;1.1.1.1#10#
# flood icmp 1.1.1.1#5#

A significant finding of our analysis has shown that the toolkit that is used to build the bot client executable is Backdoored. On execution of the toolkit, it opens a random port on the infected system in the listening mode. Also , it is found sending significant system information to the remote server . Below is the snapshot of Base-64 encoded traffic that we captured when the toolkit was launched for building the bot.


Decoding above traffic shows the info that was being sent by this toolkit


In the next part of this blog , I will talk about Darkness , Another highly prevalent DDoS Botnet on the Internet